
This is often contrasted with public-key cryptography, in which keys are generated in pairs and the transformation made by one key can only be reversed utilizing the opposite key. In words, given ciphertext \(C\) and key \(K\), the \(j\)th little bit of the plaintext is the \(j\)th bit of the ciphertext, XOR with the \(j\)th bit of the necessary thing. It’s everywhere—in disk encryption, TLS/SSL periods, VPNs, databases, and extra. AI agent safety is an identity problem, however it typically starts as a secrets and credential drawback. Do your AI brokers function utilizing static API keys, tokens, and different reusable credentials? They would possibly bypass conventional identification controls, creating a governance blind spot.
Undertake Centralized Key Administration
Its software-based implementation usually outperforms AES on gadgets with out devoted cryptographic hardware. Just like the keys to your own home, great emphasis should be placed on sustaining and securing cryptographic keys. Asymmetric-key algorithms and symmetric-key algorithms are basic types of cryptography. This article delineates the details of symmetric encryption and throws gentle on the benefits and challenges. Unprotected keys and inconsistent signing policies put your software https://chandigarhcity.info/business-contact-details/21586/SLG-Computer-Software/index.htm provide chain in danger. AppViewX Code Signing secures keys in FIPS-certified HSMs, enforces consistent signing policies throughout your CI/CD pipeline, and gives safety and DevOps full visibility into each signing occasion.
Uneven Encryption Vs Symmetric Encryption
Evaluations of open supply, multi-cloud, Kubernetes, and DevOps secrets and techniques management options for enterprise groups. The major considerations for self-use keys revolve round their era, storage, and rotation. A typical example is JWT tokens used during person authentication and authorization. These tokens store data related to the user’s session, identity, or permissions and are saved on the consumer side.
- In the case of a login, that key would be the password, which is a shared secret between the service provider and the account proprietor.
- An attacker who sees two different messages encrypted with the identical IV will know the bitwise XOR of the two messages.
- Symmetric-key encryption usually relies on the bitwise XOR (exclusive-or) operation (written as \(\oplus\)), so let’s review the definition of XOR.
- Symmetric keys often don’t follow recognizable patterns and are thus more difficult to detect than most API keys.
- To account for the reality that cryptosystems can leak plaintext size, we use equal-length messages within the IND-CPA recreation.
Enhancing User Access And Identification Administration To Deal With Modern Enterprise Danger
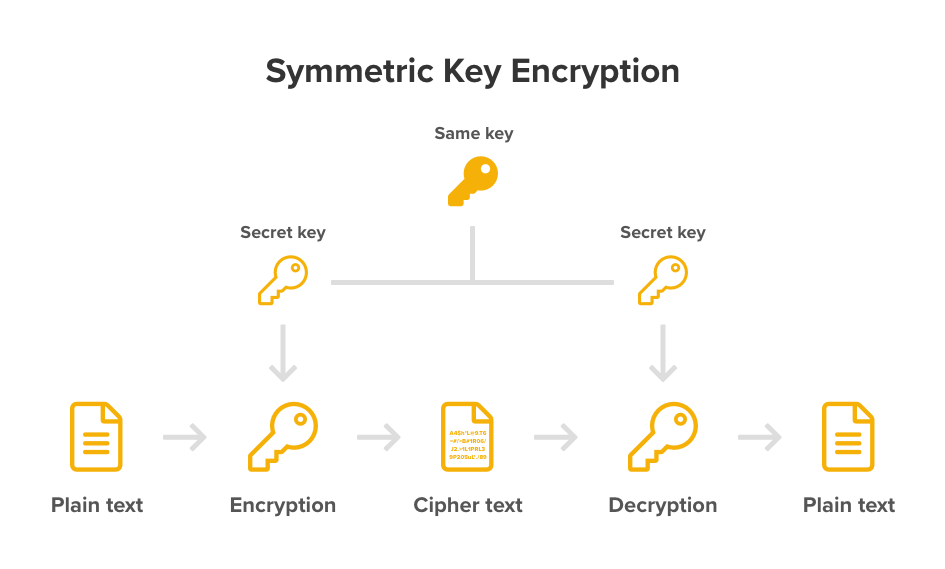
As the identical key is used for ciphering and deciphering the info sets, if the secret is passed over to unauthorized malicious customers, then the third parties can simply intercept the data units. With a malicious person getting access to the vital thing, the entire system information security comes into question. Symmetric-key algorithms should be secure when used correctly and are highly environment friendly, so they can be used to encrypt giant quantities of information with out having a adverse impact on performance. In CBC mode, if the plaintext size isn’t a multiple of 128 bits, then the final block of plaintext shall be barely shorter than 128 bits. Then the XOR between the 128-bit previous ciphertext and the less-than-128-bit final block of plaintext could be undefined–bitwise XOR only works if the two inputs being XORed are the identical size.
The symmetry of the algorithm comes from the reality that both events involved share the same key for both encryption and decryption. It works similar to a physical door the place everyone makes use of a copy of the identical key to both lock and unlock the door. A symmetric-key algorithm, identical to real doors, requires the distribution and safety of shared keys. Now, one will find the superior encryption standard algorithm being used at all places of the cyber world. With the key choices of 128, 192, 256 bits this algorithm is far more environment friendly & secure than the earlier ‘predecessors’. Though it is a https://xosokq.info/the-trading-journal-your-most-important-analytical-tool/ block-type cipher tactic, it operates within the substitution-permutation network.
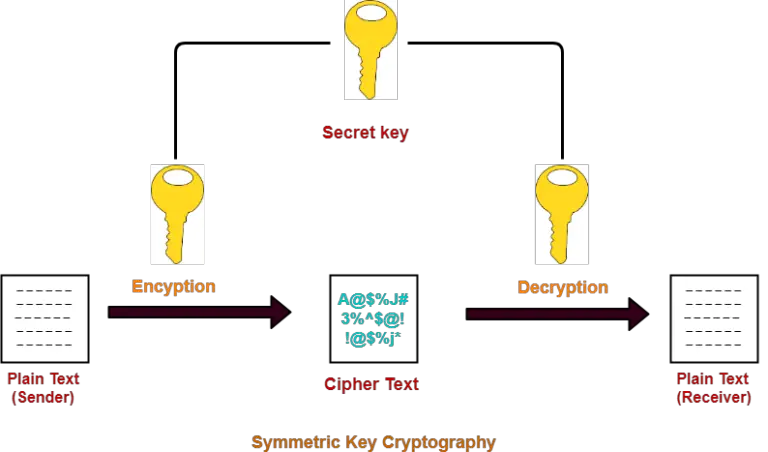
Generic secret detection requires extra sophisticated entropy-based analysis and pattern recognition to identify probably leaked symmetric keys in code repositories, logs, and configuration information. Since the secret is solely generated and used inside the application’s session, it’s ephemeral and tied directly to the applying occasion. As Quickly As the applying stops or restarts, the secret’s discarded and regenerated, making certain no delicate information persists past the runtime. A prime example is the interplay between an RFID smart card reader and the smart card itself.