
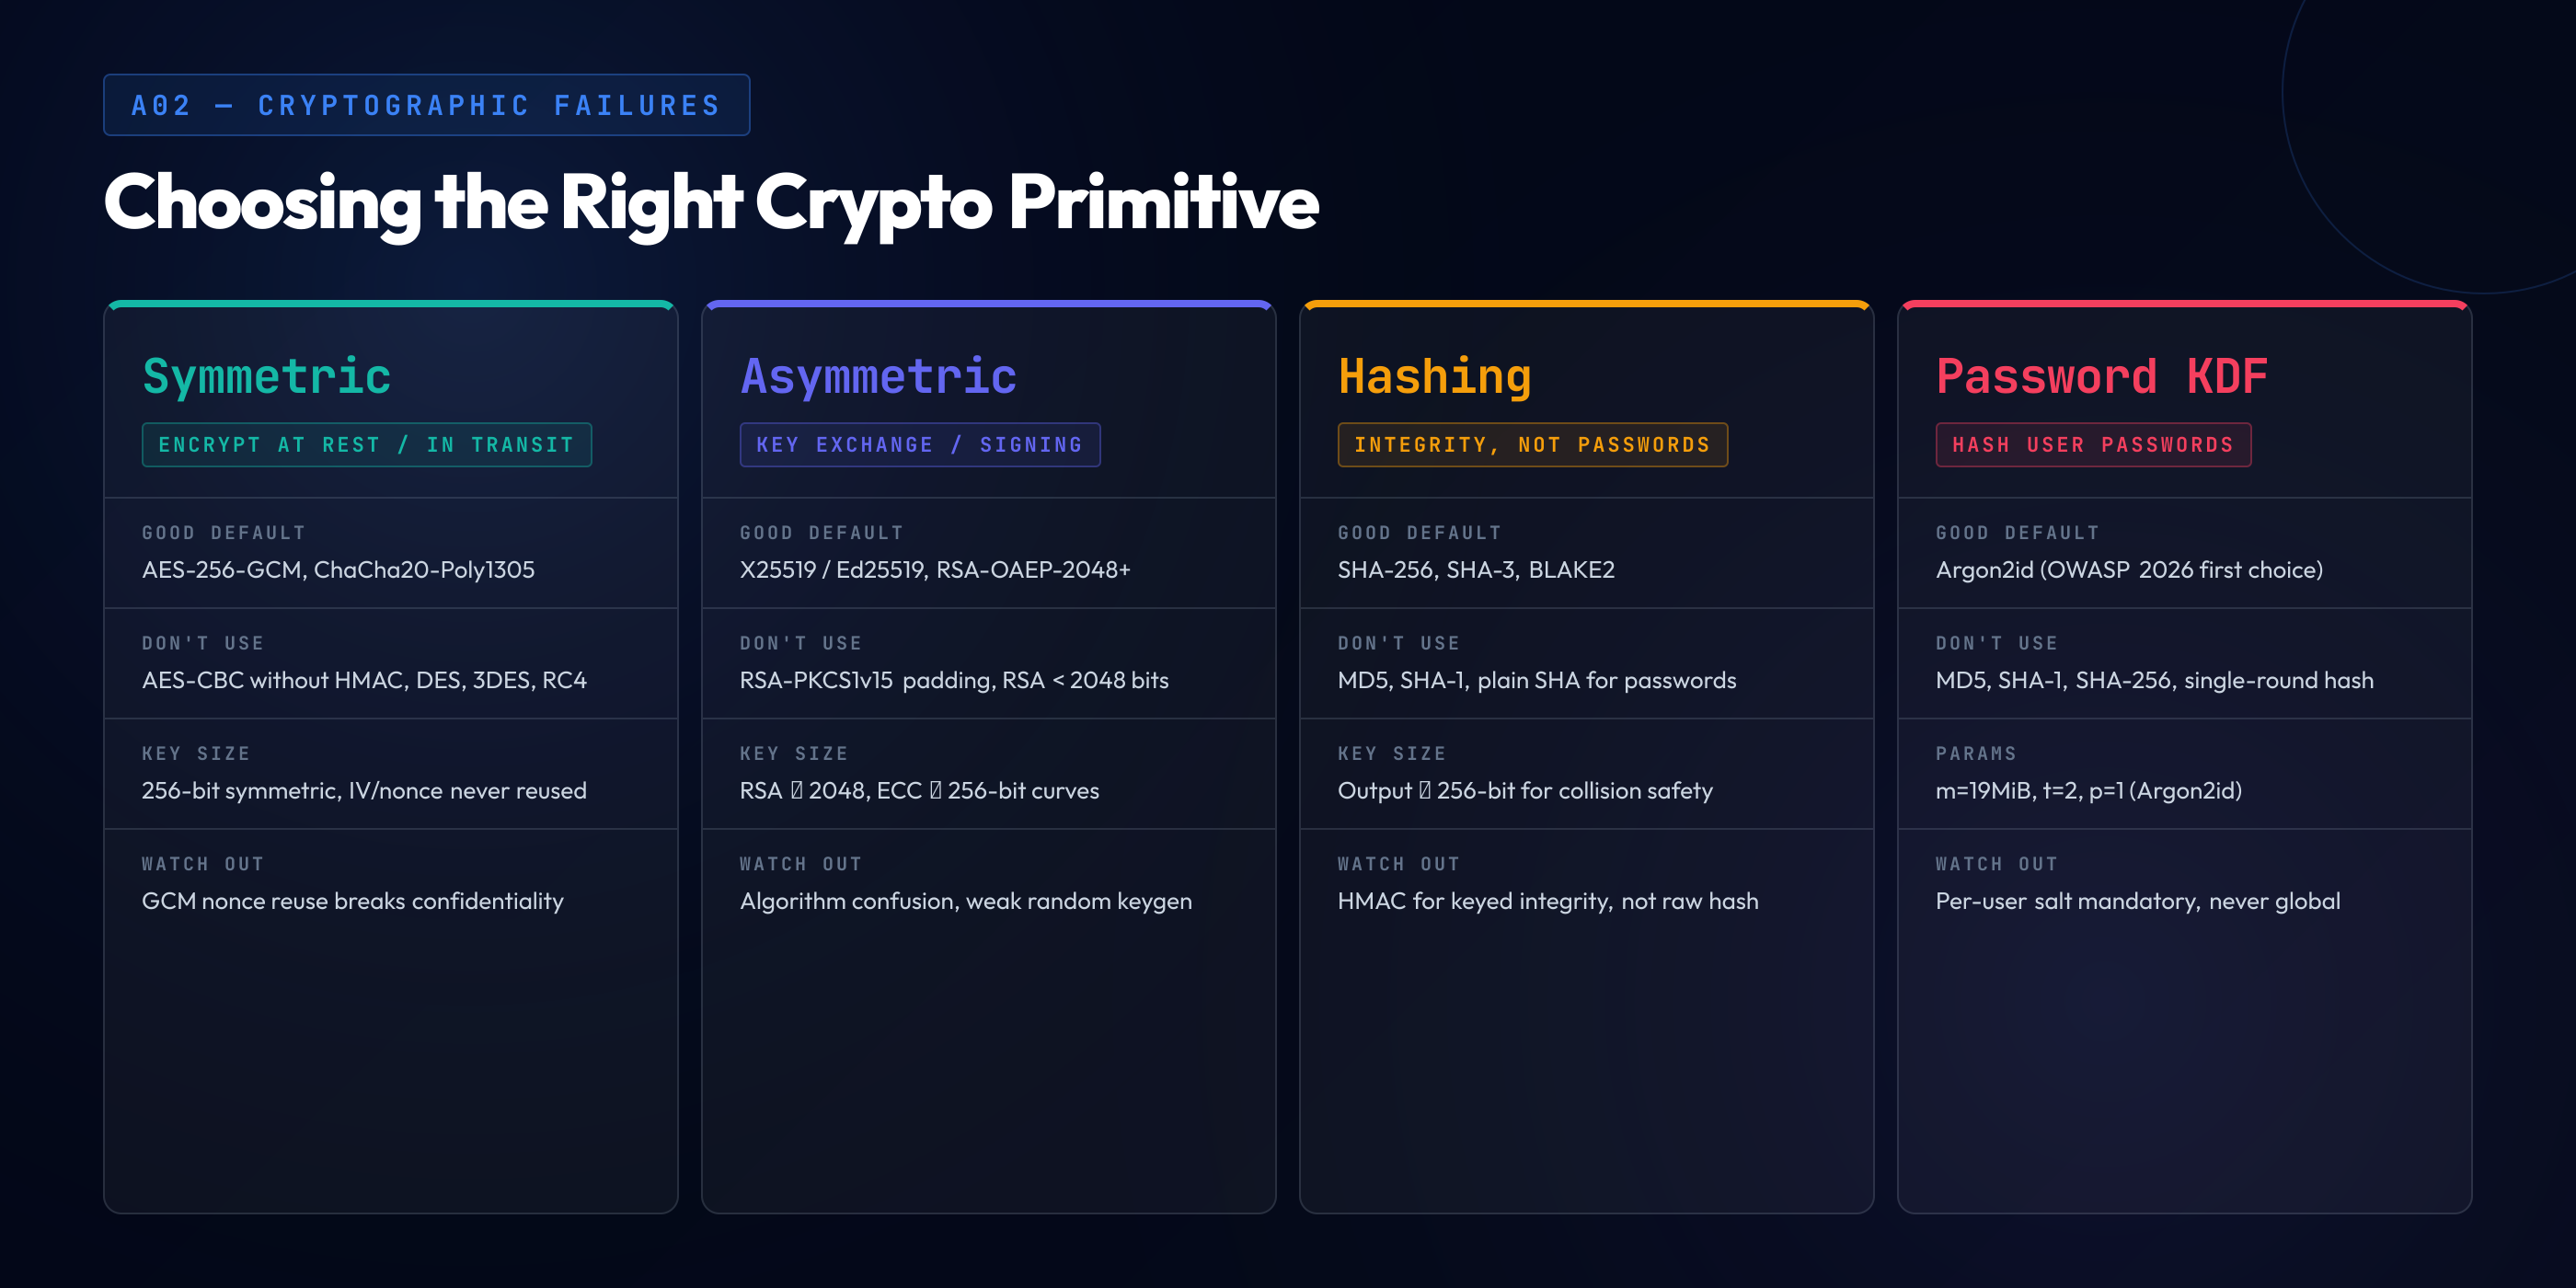
Knowledge that is encrypted utilizing the basic public key can solely be decrypted using the corresponding personal key, and vice versa. This permits for safe communication even if the public key’s identified to an attacker. Up to this point, we now have been assuming that the message wasn’t confidential, so the unique message might be transmitted as plaintext.
Tls Certificates
For instance, theword “login” is likely to happen initially of a remote loginsession, and customary headers seem initially of HTTP messages. This mayenable a recognized plaintext assault, which has a much higher likelihood ofsuccess than a ciphertext only assault. Even higher is a chosenplaintext attack, which may be enabled by feeding some info https://xosokq.info/backtesting-software-validating-your-strategy-with-history/ tothe sender that you understand the sender is prone to transmit.
Cryptographic Algorithms
- If you’re not acquainted with hash features, you probably don’t notice how crucial and pervasive they’re in cryptographic systems.
- This section is meant as an summary quite than a deep examination of the problems.
- H is the hash perform, K is the vital thing, and opad (output pad) and ipad(input pad) are well-known strings which may be XORed (⊕) with the vital thing.
- It was clearly designed with effectivity in thoughts, notably efficiency in hardware.
- The symmetric key sent over this confidential channel is called a session key.
So we begin our examine of technical approaches to networksecurity with an summary of cryptography. Avalanche uses the convention chainID-address to specify which chain an address exists on. APIs and wallets show X-Chain and P-Chain addresses in the Bech32 format that the subsequent section describes. To keep away from posting the complete TLS certificates to the P-Chain, the certificate is first hashed.
Merkle Proofs
So a random distribution of hash outputs isan essential property for these algorithms. Like RSA, it depends on amathematical problem, the discrete logarithm problem, for which noefficient solution has been discovered, and requires keys of at least 1024bits. When we are saying “cannot be read” we are going tomake some assumptions in regards to the computational capabilities and timeavailable to the attacker; more on this in a moment. Once we now have a set of cryptographic algorithms and a approach to distributekeys, we are ready to construct protocols that allow securecommunication between members.
A deep explanation of this HMAC operate is past the scope of this book. Nevertheless, this method has been proved to be safe so long as the underlying hash function H has the suitable collision-resistance properties outlined above. Observe that the HMAC takes a hash perform H that is not keyed, and turns it into a keyed hash by adding the key materials to the textual content enter to the hash. First the key (XORed with a string, ipad) is prepended to the message, which is then fed into the hash operate.